What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
The BIOS setting to look for is firmware TPM 2.0. On AMD gaming PCs, it is usually called AMD fTPM or AMD PSP fTPM. On Intel systems, look for Intel PTT or Intel Platform Trust Technology.
Enabling it may remove the TPM compatibility block without buying new hardware. It is not a guarantee that your PC qualifies for Windows 11, however: processor support, UEFI, Secure Boot capability, RAM, storage and graphics requirements still apply. Check those before changing firmware settings.


As an Amazon Associate I earn from qualifying purchases.
Check what is actually blocking the upgrade
Before entering the BIOS/UEFI, confirm the state of your security hardware and boot configuration.
Free tools Windows power users keep installed
One-click scans. No signup required.
Check TPM 2.0 with TPM Management
- Press Windows + R.
- Enter
tpm.mscand select OK. - Look for “TPM is ready for use”.
- Confirm Specification Version: 2.0.
If Windows says that a compatible TPM cannot be found, the device may simply be disabled in firmware. A TPM 1.2 device does not meet the normal Windows 11 requirement. See Microsoft’s TPM 2.0 guidance.
#1 Best Overall
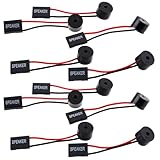
- Essential Tool: This PC motherboard internal speaker is a crucial diagnostic component for any computer build or repair. When you start your computer, the familiar boot 'beep' sound indicates normal system operation. More importantly, specific beep code patterns emitted by this BIOS alarm buzzer help diagnose hardware issues like memory errors, graphics card failures, or power supply problems
- Simple Plug and Play Installation: Installing this computer case speaker is straightforward and requires no technical expertise. It comes equipped with a standard 4-pin female connector designed to match the speaker header pins on the front panel of virtually any motherboard. The wiring is clearly indicated with red for positive and black for negative, though polarity is often interchangeable
- Durable and Reliable Construction: Built for long-term reliability, this motherboard speaker is constructed from sturdy metal and plastic materials. The robust build ensures it won't break easily during installation or from regular system vibrations. Its reliable performance means it will serve you consistently over the long term, providing clear, audible beep codes whenever you power on your PC
- Clear POST Code Audibility: In environments where external multimedia speakers are unnecessary, such as office servers, test benches, or minimalist setups, this internal PC speaker is indispensable. It allows you to hear the essential BIOS beep codes that confirm a successful boot or signal hardware faults
- Versatile Multi-Pack Value: This package includes 10 pieces of motherboard speaker offering exceptional value for frequent builders, repair shops, or IT departments. Each unit features an approximately 3-inch cable to minimize wiring clutter inside the computer case
Check UEFI, Secure Boot and the system disk
- Press Windows + R, enter
msinfo32, then press Enter. - Check BIOS Mode. The preferred result is
UEFI. - Check Secure Boot State.
- Open Disk Management by right-clicking Start.
- Right-click the disk containing Windows, choose Properties > Volumes, and check Partition style.
The system disk will generally need to be GPT before you switch fully to UEFI and enable Secure Boot. You can also check disks in PowerShell:
Get-Disk | Format-Table Number, FriendlyName, PartitionStyle, OperationalStatusMicrosoft’s MBR2GPT documentation explains the relationship between MBR, GPT and UEFI.
Back up before changing firmware
Make a current backup of important files and, if possible, prepare a Windows recovery drive or installation USB. Photograph your existing boot and storage settings so you can restore them if necessary.
If BitLocker or Windows device encryption is active, make sure you have the recovery key and suspend protection before changing TPM, boot mode or partition configuration. Firmware changes can trigger a BitLocker recovery prompt. Do not select Clear TPM as a routine troubleshooting step: clearing it can disrupt BitLocker, Windows Hello and other protected credentials. You normally want to enable firmware TPM, not erase it.
Enter your motherboard’s UEFI/BIOS
From Windows, the most reliable route is:
- Open Settings > System > Recovery.
- Under Advanced startup, choose Restart now.
- Select Troubleshoot > Advanced options > UEFI Firmware Settings > Restart.
On some Windows 10 installations, the path begins at Update & Security > Recovery. You can also press the firmware key during startup. Common keys include Delete, F1, F2, F10, F11, F12 and Esc, but the correct key depends on the motherboard or PC manufacturer. Microsoft documents additional ways to boot to UEFI or legacy BIOS.
Rank #2
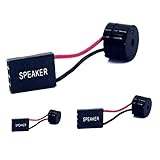
- [Quick PC Diagnostic Tool] Is your new PC build showing a black screen? This motherboard speaker translates silent hardware failures into clear BIOS beep codes. Instantly identify if your RAM, CPU, or GPU is causing the boot failure without guessing.
- [Essential for DIY PC Builders] Modern motherboards often lack built-in audio alerts. Plugging in this mini piezo buzzer before your first boot ensures you hear the satisfying “single beep” of a successful POST, giving builders immediate peace of mind.
- [Universal 4-Pin Header Compatibility] Wondering if it fits your board? It features a standard 4-pin female connector (with 2 active wires) that perfectly matches the “SPEAKER” or “SPK” front panel header on almost all ATX, Micro-ATX, and Mini-ITX motherboards.
- [Clean Wiring & Loud Alarm] Designed with an approx. 3-inch cable, it is long enough to easily plug into the motherboard but short enough to reduce PC case wiring clutter. The premium piezo element delivers a loud, crisp beep that is impossible to miss.
- [Valuable 3-Pack for IT Repair] Includes 3 internal BIOS buzzers in one pack. Perfect for IT technicians keeping spare diagnostic tools in their repair kits, or PC enthusiasts testing multiple rigs. A cost-effective solution to save hours of troubleshooting.
Enable firmware TPM 2.0
BIOS menus vary by manufacturer, model and firmware version. Use these paths as a map, not as universal instructions.
| Platform | Possible setting names |
|---|---|
| AMD | AMD fTPM, AMD PSP fTPM, Firmware TPM, AMD fTPM switch |
| Intel | Intel PTT, Intel Platform Trust Technology, TPM Device |
| Any platform | Security Device, Security Device Support, TPM State, Trusted Computing |
| OEM laptop or desktop | Firmware TPM, TPM Device, Security Chip, Trusted Platform Module |
AMD examples
Look under menus such as:
Advanced > AMD fTPM configuration > Enable Firmware TPMAlternatively, check Advanced > Trusted Computing for Security Device Support: Enabled. Some boards use AMD fTPM switch: Enabled or AMD PSP fTPM: Enabled.
Intel examples
Possible locations include:
Advanced > PCH-FW Configuration > Intel Platform Trust Technology: EnabledYou may instead find Intel PTT under Security > Trusted Computing, or a setting called TPM Device.
Enable only the TPM-related option. Avoid changing voltage, overclocking, storage or unrelated boot settings. Choose Save & Exit—often F10—and restart.
Verify TPM after restarting
- Run
tpm.mscagain. - Confirm that the TPM is ready for use.
- Confirm Specification Version: 2.0.
- Run Windows Update or Microsoft’s PC Health Check again.
If the only failure was a disabled TPM, this may remove the block. If the PC still fails, check the processor, boot mode, Secure Boot capability and other requirements rather than repeatedly changing BIOS settings.
Rank #3
- Type: 5PCS PC computer motherboard alarm buzzer, length 2.3 inches
- Uses: The sound made by the buzzer is used to determine the working status of the motherboard.Easy to install, 4-pin female connector, plug and play, easy to plug into the speaker connector on the front panel of the motherboard
- Wiring: red positive pole, black negative pole (in fact, as long as the interface is connected to the speaker, both positive and negative poles can be used)
- How To Use: After turning on the computer, we will hear the familiar "beep" sound, usually indicating that the computer is working properly, the sound comes from this buzzer. If it is not normal, you can judge the fault by its sound
- 100% brand new and high quality
Why UEFI, GPT and Secure Boot may also matter
TPM and Secure Boot are related but different. TPM protects security keys and records trusted measurements; Secure Boot controls which boot software is allowed to run.
Quick wins for a faster PC:
Fix the driver behind crashes, sound loss and screen glitchesFind Drivers →Repair Windows errors before they cause bigger problemsFix Now →Microsoft requires UEFI firmware that is Secure Boot-capable. Secure Boot does not necessarily have to be enabled in every upgrade scenario, although it improves boot security and some games or anti-cheat systems may require it. Read Microsoft’s Windows 11 and Secure Boot guidance.
If msinfo32 reports BIOS Mode: Legacy and the Windows disk is MBR, do not immediately disable CSM or switch the firmware to UEFI. That can make the existing Windows installation unbootable.
Convert an eligible system disk with MBR2GPT
- Back up your files and confirm that the motherboard supports UEFI.
- Suspend BitLocker or device encryption.
- Open Command Prompt as administrator.
- Identify the Windows system disk, especially if multiple disks are installed.
- Validate the layout:
mbr2gpt /validate /allowFullOSOnly proceed if validation succeeds. Then run:
mbr2gpt /convert /allowFullOS- Restart directly into firmware setup.
- Change boot mode to UEFI.
- Disable CSM or Legacy Boot if required by your firmware.
- Enable Secure Boot if needed.
- Save and restart.
- Confirm in
msinfo32that BIOS Mode now saysUEFI.
MBR2GPT is a Microsoft-supported, non-destructive conversion route on eligible layouts, not a guarantee against every failure. Validation can fail when a disk has too many primary partitions, extended or logical partitions, insufficient space for the EFI System Partition, invalid boot configuration or active encryption. It is intended for the operating-system disk, not arbitrary data disks.
Windows 11 eligibility checklist
Enabling TPM is only one part of the decision. Microsoft’s current Windows 11 requirements include:
The Tool Desk
Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →Outbyte PC Repair FREERepair Windows errors before they cause bigger problemsFix Now →- A compatible 64-bit processor running at 1 GHz or faster with at least two cores.
- At least 4 GB of RAM.
- At least 64 GB of storage.
- UEFI firmware that is Secure Boot-capable.
- TPM 2.0.
- DirectX 12-compatible graphics hardware with a WDDM 2.0 driver.
- A display meeting Microsoft’s minimum specifications.
- Applicable Windows edition, internet connectivity and Microsoft account requirements during setup.
Use Windows Update, PC Health Check and Microsoft’s official Windows 11 upgrade guidance for the current verdict. Windows 10’s ordinary free support ended on October 14, 2025, but that does not mean every older gaming PC can be made eligible through firmware changes.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Troubleshooting
There is no TPM option
The setting may be hidden under Advanced, Security or Trusted Computing. Check the exact motherboard or PC model in its manual and look for a BIOS/UEFI update from the manufacturer. Some older systems need a vendor-specific physical TPM module, but modules are not universal: the header, pin layout and firmware support must all match.
Manufacturer examples include ASUS, MSI, Gigabyte, Dell, HP and Lenovo.
TPM is enabled, but Windows 11 still refuses the PC
Recheck that tpm.msc reports version 2.0, then inspect msinfo32, Secure Boot capability, CPU compatibility, RAM, storage, graphics support and Windows edition. Give Windows Update or PC Health Check time to refresh its assessment. Do not treat registry bypasses or unsupported installation methods as the normal fix; they can affect support, updates, drivers, security features and recovery.
Windows will not boot after enabling Secure Boot
The most common cause is a Legacy/CSM installation on an MBR disk. Re-enter firmware setup and temporarily restore the previous boot mode or re-enable CSM so Windows can start. Confirm the disk and boot mode, then use MBR2GPT only after backing up and validating the configuration. Do not repeatedly clear TPM data or Secure Boot keys.
If the machine cannot boot at all, use Windows Recovery or installation media and consult the motherboard manufacturer’s documentation.
BitLocker asks for a recovery key
TPM, Secure Boot and boot-mode changes alter measured-boot information, so BitLocker may request its recovery key. This is why locating the key and suspending protection before the change matters. Do not delete encryption data or clear the TPM merely to dismiss the prompt.
The firmware warns about TPM keys
Distinguish between enabling firmware TPM and clearing it. Enabling or activating fTPM/PTT is normally the intended action. Clearing TPM removes stored keys and can affect BitLocker, Windows Hello and other credentials. Stop and verify your backups and recovery key before accepting a clear or reset operation.
When a BIOS setting will not help
A firmware switch cannot add an unsupported CPU instruction set, missing UEFI capability, insufficient memory, incompatible graphics hardware or a motherboard feature that does not exist. If the processor fails Microsoft’s compatibility check, enabling TPM will not make the PC officially eligible.
If the BIOS offers no firmware TPM option, check for a manufacturer BIOS update and the board manual. A discrete TPM may work only when the exact module is supported. Buying Windows 11, a random TPM module or a new gaming PC before identifying the failed requirement is usually the wrong first step.
If your goal is a particular game rather than the operating-system upgrade, check that game’s own requirements. Some anti-cheat systems separately require TPM 2.0, Secure Boot or both.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problems



