Do these 3 things before closing this tab:
1Scan for outdated or missing drivers - takes under a minute2Repair Windows errors before they cause bigger problems3Fix the driver behind crashes, sound loss and screen glitchesDMA cheating abuses a normal PC feature. Direct Memory Access lets devices such as graphics cards, storage controllers, network adapters, and sound cards transfer data without the CPU copying every byte. A DMA cheat misuses a DMA-capable PCIe device to obtain unauthorized access to game-related memory—sometimes sending that information to a second computer for analysis.
That can make a cheat harder for conventional anti-cheat software to observe, but it does not make the attack invisible or permanently defeat modern security. IOMMU-based DMA remapping, correct pre-boot protection, firmware integrity, device checks, server telemetry, and gameplay analysis all matter.
As an Amazon Associate I earn from qualifying purchases.
DMA is not inherently a cheat
DMA, or Direct Memory Access, is a standard computer capability. A device can transfer data to or from system memory through hardware pathways instead of requiring the CPU to handle every individual byte. That reduces overhead and helps high-throughput devices perform efficiently.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEFix the driver behind crashes, sound loss and screen glitchesFind Drivers →The same principle applies to legitimate peripherals, forensic tools, security-research equipment, and maliciously configured hardware. A “DMA card” is therefore an informal description, not one standardized product category. The relevant question is whether a device has unauthorized access to memory, not whether it uses DMA.
#1 Best Overall
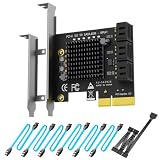
- 6-PORT SATA EXPANSION CARD: Adds 6 SATA III (6Gbps) drives to your desktop at once, turning one PCIe x4 slot into a 6-bay storage pool for unRAID, TrueNAS, ZFS, Proxmox or Windows Storage Spaces software RAID. Hardware RAID is not supported.
- 277MB/S ON EVERY PORT: PCIe 3.0 X2 upstream runs at 16GT/s, and each of the 6 SATA ports delivers up to 277MB/s, so large multi-drive transfers, media libraries and backup jobs finish fast with no bottleneck.
- NO DRIVER, WIDE COMPATIBILITY: Plug and play on Windows (except XP), Mac OS, Linux and NAS systems. Set SATA mode to AHCI in BIOS or UEFI before first install. This is a data storage HBA and does not boot an operating system.
- 6 BUILT-IN LED INDICATORS: A steady red LED means the drive is powered, a flashing LED means it is reading or writing, so you can check every SATA drive at a glance without opening the case.
- FITS X4/X8/X16 SLOTS, FULL KIT INCLUDED: Ships with 6 x SATA III cables (350mm/13.5in), a 1:5 SATA power splitter cable, and both a 12cm regular and an 8cm low-profile bracket for any PC or NAS case.
Microsoft describes Windows Kernel DMA Protection as using an IOMMU to control DMA-capable devices and apply DMA remapping to compatible hardware. Relevant platform technologies include Intel VT-d and AMD-Vi.
Microsoft’s Kernel DMA Protection documentation explains the platform requirements.
What is a DMA cheat?
A DMA cheat uses a specially configured or compromised device to read information from a gaming computer’s memory outside the usual process and driver model. That information might include game-state data that conventional software would not be allowed to inspect directly.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
The extracted data can be analyzed locally or sent to another computer. Depending on the implementation, the resulting assistance may appear as an external radar, information overlay, targeting aid, or other form of unfair knowledge. This article describes the architecture defensively; it does not provide firmware, wiring, memory-offset, or evasion instructions.
Riot has publicly described advanced cheating communities using DMA to rebroadcast memory to another computer for processing. Its explanation also emphasizes that DMA-capable hardware itself is widely used legitimately.
Riot’s explanation of Vanguard’s architecture discusses the second-computer model, while its DMA security overview describes the underlying memory-access risk.
Why a second computer can help a cheat
A conventional cheat usually runs on the same operating system as the game. Anti-cheat software can look for suspicious processes, injected modules, drivers, handles, memory changes, windows, and files.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchWindows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallRank #2

- RIITOP USB PCIe to 20Pin+ Type-E Card is a PCIe x1 interface to 1x 20Pin (19+1xempty) USB 3.0 header + 1x Type-E (A Key) USB C Header expansion card. 1x 20Pin (19+1xempty) USB 3.0 header will extend to 2x USB-A ports on front panel of Desktop PCs . 1x Type-E (A Key) USB C Header will expand 1x USB-C Port. You may add 2x 5Gbps max USB-A ports and 1x USB-C Port only via 1x PCI-e Slot on your old motherboard
- [Built-in 5Gbps Chipset With Heatsink] RIITOP USB 3.0 PCIe Adapter adopts VIA VL805, total 5Gbps bandwidth. The advanced Heatsink will help the chipset working in lower temperature, avoid having any issues with reliability due to overheating
- Hardware Requirement: RIITOP USB Expansion Card adopts PCIe x1 design, it can work on PCIe 3.0/4.0 x1, X4, X8, X16 slot, but do not work on any PCI slot. And coming with Both full-size and Half-size brackets will work on Standard Size and Mini PCs
- Easy to install: RIITOP PCIe to 20Pin + Type-E Host Internal card can be inserted to PCIe slot on MB, no additional power supply to connect. Please Note: The card can not be connected with any External USB Device directly, You may have 20pin or Type-E Front Panels to work with it together
- Compatible OS: Plug and Play on Windows 11, 10, 8.x (32/64bit) and Windows Server 2012, 2012R2, 2016, 2019, 2022 systems. But Need to Install Driver on Windows XP, Vista, 7 (32/64bit) and Windows Server 2003, 2003R2, 2008, 2008R2 (32/64bit) systems
In a conceptual two-computer arrangement, the gaming PC contains the game, operating system, anti-cheat, and DMA-capable device. The device obtains data from the gaming system, while a separate analysis computer processes the information:
Game PC                         Analysis PC
├─ Game                         ├─ External processing
├─ Operating system             └─ Assistance display or output
├─ Anti-cheat
└─ DMA-capable device
       │
       └── memory data or signals
Moving analysis elsewhere can reduce the number of suspicious software artifacts visible on the gaming PC. It does not make the attack magically undetectable. The physical device, firmware, boot state, memory-access behavior, configuration, account activity, and gameplay outcomes can all remain relevant signals.
DMA cheats versus conventional cheats
| Category | Typical execution location | What defenders may inspect | Main limitation |
|---|---|---|---|
| User-mode software cheat | Inside the game’s operating system | Processes, modules, windows, handles, files, and memory activity | More visible to ordinary software inspection |
| Kernel-mode cheat | Privileged operating-system driver or kernel | Drivers, signatures, integrity, vulnerable-driver use, and kernel behavior | Requires privileged software and leaves system-level evidence |
| DMA-assisted cheat | External or specially configured hardware | Device state, IOMMU configuration, firmware, boot integrity, hardware behavior, and gameplay | Depends on physical access and platform configuration |
| Server-side manipulation | Network or server boundary | Protocol validation and authoritative game logic | Strong server design can prevent many, but not all, attack classes |
| Game exploit | Game logic or an unintended edge case | Server validation, replay evidence, and bug reports | Usually requires a developer fix rather than anti-cheat detection alone |
FACEIT’s anti-cheat documentation makes the important distinction between cheating and vulnerabilities in game logic or server behavior.
Why DMA is difficult to detect
It operates outside the normal process model
A software anti-cheat generally observes what happens through the operating system. A device performing DMA may request memory access independently of ordinary CPU-mediated process APIs. That reduces the usefulness of searches focused only on suspicious programs or injected code.
Free tools Windows power users keep installed
One-click scans. No signup required.
The attack can involve early boot
Security software cannot automatically observe every event that happened before it loaded. A device or firmware component that gains an advantage during early boot may operate before the operating system and anti-cheat driver are fully active.
Riot has reported that certain motherboard firmware implementations indicated that pre-boot DMA protection was enabled even when the IOMMU had not been correctly initialized during the earliest part of boot. That could create a window for hardware-assisted attacks. The report concerns particular implementations, not every motherboard or every player.
Riot’s motherboard security update discusses the issue, manufacturer advisories, and firmware remediation involving vendors including ASUS, Gigabyte, MSI, and ASRock.
Rank #3

- Quad Port RS232 (4S) PCI Express (PCIe) Host Adapter, PCI Express Gen1, Gen2, Gen3 expansion slot compatible (x1, x2, x4, x8, x16 lane)
- 4 x Full 9-wire Male RS232 DTE industry standard pinout, Enhanced 16550 / 16650 / 16750 / 16950 UART modes (256 byte TX & RX FIFO)
- ±15 kV ESD and short-circuit protected RS232 transceiver, Hardware Flow Control (RTS & CTS), Low or Full Height mounting bracket support
- 4 Port HD44M to 4xDB9M Cable Included (12" length), 7' Low Smoke Zero Halogen (LSZH) Molded Cables (Optional)
Legitimate hardware creates ambiguity
Graphics, networking, audio, storage, and other devices commonly use DMA. Blocking every DMA-capable device would disrupt normal computing. Defenders must distinguish unauthorized behavior from ordinary hardware operation without assuming that a PCIe device is malicious simply because it can use DMA.
IOMMU: the security desk for system memory
The simplest analogy is a building. A DMA-capable device is someone asking to enter. The IOMMU is the security desk that decides which rooms the device may access. DMA remapping translates or restricts the addresses presented by the device, limiting it to approved memory regions.
Without effective isolation, a device may be able to request access to raw physical memory. With correctly configured IOMMU protection, the device is constrained by mappings established by the platform and operating system.
IOMMU is foundational, but it is not an anti-cheat system. It does not prove that a player is honest, identify every malicious driver, or prevent all game exploits. Protection also depends on correct firmware initialization, motherboard design, CPU support, operating-system configuration, and driver behavior.
A BIOS menu that says an option is enabled is not always conclusive evidence that the entire pre-boot security chain worked correctly. Firmware bugs can produce an apparently secure status while leaving an implementation weakness.
The pre-boot DMA problem
Pre-boot protection matters because the earliest portion of startup is a trust boundary. If a device can access memory before the operating system and anti-cheat components are active, later software may have difficulty proving what occurred or restoring trust in the system.
This is why a firmware update may be more important than a game patch. A game update can change launch checks or detection logic, but it cannot necessarily repair a motherboard’s initialization behavior. The correct fix may require a BIOS update from the motherboard manufacturer.
Rank #4
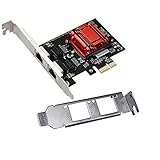
- Supports Windows 7/8/2000/XP/Vista/Windows Server 2003/2008/2012; Novell Netware 5.x/6.x; Linux; FreeBSD 7.x or later; DOS; SCO Open Server; UnixWare / OpenUnix 8; Sun Solaris x86; OS Independent Vmware ESX (Does not support VMware ESXi 7.0 or above)
- PCI Express 2.1. 2.5 GT/s x1 Lane. Compatible with x1, x2,x4, x8, x16 standard and low-profile PCI Express slots.
- Compatible with IPMI pass-through (SMBus or NC-SI), iSCSI boot, WoL, PXE remote boot, VLAN filtering
- Support Network Management Protocol (SNMP) and Remote Network Monitoring (RMON).
- Imported alloy heat sink , can effectively remove excess heat , keep the network card at normal operating temperature and double stable operation
Do not generalize a vendor advisory to every board. The affected model, firmware version, CPU platform, and publisher policy matter. A claim that “all motherboards are vulnerable” or that one BIOS setting guarantees protection is too broad.
How Vanguard and other anti-cheat systems respond
Riot’s public material describes a layered response involving:
Recommended Free Tools
- TPM 2.0: a hardware-backed location for cryptographic keys and trust-related measurements.
- IOMMU protection: a boundary governing how PCIe devices access system memory.
- Pre-boot security: protection that must be initialized correctly before the operating system loads.
- Hardware and firmware checks: measures intended to identify configurations that cannot be trusted.
- System restrictions: refusal to launch or access restrictions when security requirements are not met.
- BIOS remediation: cooperation with motherboard manufacturers to address firmware weaknesses.
These measures do not mean that every DMA device has been physically destroyed or made universally useless. A protected game may reject a particular configuration, a firmware approach may stop functioning, or IOMMU enforcement may prevent the device from accessing the memory it needs. Those outcomes are different from hardware damage.
Similarly, a Vanguard restriction does not necessarily prove that an account was conclusively identified as cheating. Riot says some restrictions reflect an untrusted or suspicious system configuration associated with hardware-cheat bypasses. Players should treat the exact warning and official support guidance as more meaningful than social-media claims.
Can DMA cheats still be detected?
Yes—but prevention, detection, attribution, punishment, and appeal are different tasks.
- Hardware and firmware: Device enumeration, firmware characteristics, boot measurements, and IOMMU state can provide signals.
- Operating-system state: Anti-cheat can inspect drivers, integrity controls, virtualization conditions, and other system configuration.
- Client and kernel components: Higher-privilege software can observe more of the operating system, though it also raises greater privacy and security concerns.
- Server telemetry: Authoritative validation, encrypted networking, movement checks, visibility rules, and rate limits can reduce what the client is trusted to decide.
- Gameplay analysis: Repeated pre-aiming at unseen opponents, implausible reactions, unusual target selection, or statistically unlikely information advantages may justify investigation.
- Reports and review: Player reports and replay analysis can add context, but unusual gameplay alone is not definitive proof.
Gameplay analytics are probabilistic. A remarkable clip, overlay, or warning should not by itself be treated as proof that a specific player cheated.
Legitimate DMA research: PCILeech
PCILeech is a useful example of why the technology should not be equated automatically with cheating. Its official documentation describes PCIe-based memory acquisition and read/write capabilities without requiring a target-side driver, alongside forensic and security-research use cases.
Best Value

- 【7 ports PCIe USB card】 There is a 2-phase independent power supply module, which can feed one interface per output port to escape power shortage. Can operate without an external or auxiliary power supply; the seven interfaces operate independently and do not affect each other. Seven USB 3.0 Type A ports can be added externally to the PC case. Note: Not compatible with PS3/PS4.
- 【High Speed Transmission】USB3.0 theoretical speed up to 5Gbps, provides 10 times faster transmission speed than USB2.0. This usb expansion card enables quick access to files and transfer of HD movies, photos, music, etc.
- 【Stable power supply】The usb pcie card adopt NEC720201&NEC720210 chip. The USB interface can supply 5V2A power to external devices. Solid capacitors with good performance are used for low impedance, low temperature stability, and high temperature wave resistance.
- 【7 independent solid capacitors】Each interface has a stable voltage solid capacitor to ensure a stable power supply. The dielectric material of the solid capacitors is made of conductive polymer material, which has the advantages of high stability, long life, and low ESR (faster charging and discharging speed).
- 【Wide compatibility】 PCI-E X1 X4 X8 X16 compatible. Note: Not compatible with older PCI, backward compatible with USB 2.0 / 1.1, 64-bit and 32-bit Windows 11 / 10 / 8 / 7 / XP / Linux, not Mac compatible. Note: WIN8 and WIN10/11 users do not need to install the drive; XP and WIN7 users can download, unzip, install, and complete. (The corresponding installation directory for CD is DRIVERSǐ201R30230.EXE.)
Those capabilities are highly sensitive and must be used only on systems for which the operator has authorization. The project also documents limitations when IOMMU/VT-d and modern virtualization-based protections are enabled. A legitimate research tool is not automatically a game cheat, just as a DMA-capable peripheral is not evidence of misconduct.
The kernel anti-cheat and privacy trade-off
User-mode anti-cheat is less privileged and generally easier to isolate, but it has less visibility into kernel and hardware-assisted threats. Kernel-level anti-cheat can observe or control more of the operating system, potentially improving resistance to privileged cheats and vulnerable drivers.
The trade-offs are substantial:
- Greater visibility versus greater system privilege.
- Stronger enforcement versus compatibility failures.
- Hardware-backed identity versus privacy concerns.
- Rapid security response versus firmware quality and false-positive risk.
- Proprietary detection logic versus independent auditability.
Riot describes Vanguard as including a client, kernel driver, and platform components, while acknowledging the privacy and security concerns that come with kernel-mode software. A 2024 academic paper evaluated several kernel anti-cheat systems against rootkit-like characteristics and reported that Vanguard and FACEIT Anti-Cheat exhibited such behavior under its methodology. That finding should be attributed to the paper’s criteria; it is not the same as a universal legal or technical classification of those products as rootkits.
See the academic analysis alongside Riot’s privacy and security explanation.
Why server-side design still matters
Anti-cheat cannot compensate for a game that trusts the client too much. Competitive games should validate important state on the server, protect network communication, enforce plausible movement and visibility rules, and investigate statistical anomalies.
Server-side defenses also help with exploits that are not DMA cheats. A game bug, unintended mechanic, or server flaw generally requires a developer fix. FACEIT’s documentation explicitly separates these game-logic problems from the role of anti-cheat.
What players should do when a game reports missing protection
- Record the exact game, anti-cheat product, warning text, motherboard model, CPU platform, Windows edition, and firmware version.
- Check the game publisher’s official support page for that exact message.
- Check the motherboard manufacturer’s BIOS releases and security advisories.
- Update firmware only through the manufacturer’s documented procedure.
- Configure TPM, Secure Boot, virtualization, and IOMMU-related options according to official guidance. Labels vary between vendors and Intel and AMD platforms.
- Do not disable IOMMU, Secure Boot, TPM, or virtualization-based security merely to make an untrusted peripheral work.
- If the system becomes unstable, use the motherboard vendor’s documented recovery process and contact official support.
- Avoid third-party bypass tools, “DMA firmware,” HWID spoofers, and unauthorized driver loaders. They can create security, stability, and account risks.
There is no universal test that proves a system is protected for every game and configuration. Windows Kernel DMA Protection, motherboard pre-boot behavior, and game-specific anti-cheat checks are related but distinct layers.
What DMA cheating means for the future
DMA cheating is best understood as a hardware-assisted attack against the client’s trust boundary. It is harder for conventional process scanning to observe, but it is constrained by platform security, firmware correctness, physical access, device behavior, server design, and gameplay evidence.
The most accurate conclusions are narrower than the usual headlines: DMA is legitimate technology abused by a real class of cheats; IOMMU and correct pre-boot initialization are central defenses; TPM supports trust but does not itself prevent DMA; and anti-cheat restrictions do not always equal a proven cheating attribution.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




