Act quickly, but do not panic. Stop clicking messages or links related to the suspected hack, move to a trusted or known-clean device, and use only the game platform’s official recovery page or app. If you can still sign in, change the password, end unfamiliar sessions, restore recovery settings, enable multifactor authentication, and inspect purchases, messages, linked accounts, and payment methods. If you are locked out, recover the email account tied to the game account first when necessary, then use the provider’s official compromised-account process.
This guide is general consumer guidance for the United States. Menus, recovery delays, eligibility, and support options vary between Steam, PlayStation Network, Xbox, Nintendo, Epic Games, Riot, Discord, Twitch, Google, Microsoft, Apple, and other services.
As an Amazon Associate I earn from qualifying purchases.
First: do these things in the next 10 minutes
- Stop interacting with the suspected attacker. Do not reply, click their links, open attachments, call phone numbers in messages, or accept offers from someone claiming they can “recover” the account.
- Use a trusted device. If the computer or phone may have malware, use a different device if possible. Otherwise, update trusted security software and scan the device before entering a new password.
- Open the provider’s site or app yourself. Type the known address, use a previously installed official app, or navigate from the provider’s main website. Do not use a recovery link sent by an alleged support agent.
- Call the bank or payment provider immediately if you see unauthorized purchases, transfers, payroll changes, or other financial activity.
- Save evidence. Screenshot login alerts, changed-account notices, suspicious messages, purchases, usernames, phone numbers, URLs, wallet addresses, and dates before deleting anything.
An account takeover is usually recoverable. The safest order is contain, recover, secure, inspect, protect connected accounts, report, and warn contacts.
How to tell whether your account was probably compromised
One unusual login does not always mean an attacker successfully entered the account; it can be a location error, a shared device, or an old session. Treat the situation seriously, however, if you see several of these signs:
#1 Best Overall

- Compact Mouse: With a comfortable and contoured shape, this Logitech ambidextrous wireless mouse feels great in either right or left hand and is far superior to a touchpad
- Durable and Reliable: This USB wireless mouse features a line-by-line scroll wheel, up to 1 year of battery life (2) thanks to a smart sleep mode function, and comes with the included AA battery
- Universal Compatibility: Your Logitech mouse works with your Windows PC, Mac, or laptop, so no matter what type of computer you own today or buy tomorrow your mouse will be compatible
- Plug and Play Simplicity: Just plug in the tiny nano USB receiver and start working in seconds with a strong, reliable connection to your wireless computer mouse up to 33 feet / 10 m (5)
- Better than touchpad: Get more done by adding M185 to your laptop; according to a recent study, laptop users who chose this mouse over a touchpad were 50% more productive (3) and worked 30% faster (4)
- You are suddenly locked out or your password no longer works.
- You receive an unrequested password-change, username-change, email-change, or recovery-phone notification.
- A sign-in appears from an unfamiliar device, browser, location, or time.
- Friends, teammates, followers, or coworkers received messages, links, trade requests, or money requests that you did not send.
- Your display name, profile, avatar, privacy settings, linked accounts, or two-step-verification methods changed.
- Game purchases, subscriptions, wallet balances, item trades, marketplace activity, or payment methods changed without your permission.
- New forwarding rules, filters, automatic replies, signatures, delegated access, or connected applications appear in the email account attached to the game account.
The FTC identifies unexpected password or username changes, unfamiliar sign-ins, lockouts, and messages sent without permission as common signs of account takeover. If you see one of them, assume the account may be exposed until you verify otherwise.
Do not use the attacker’s “support” channel
Attackers often follow a real compromise with a second scam. They may impersonate platform support, a moderator, a tournament organizer, a friend, or a security employee. They may ask for a verification code, backup code, password, recovery key, device approval, payment, or remote access to your computer.
Do not provide any of those things. Legitimate support should not need your password or one-time authentication code. Google specifically warns that unsolicited calls, texts, or emails claiming to be Google Security are scams and says it will not ask for a password, verification code, or device approval by phone. The same principle applies to game platforms and other account providers: start the contact yourself through the official website or app.
Outdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchPC Slower Than It Used to Be?
A free scan shows the junk files, broken settings and background clutter dragging Windows down - then fixes them in one click.Free scan · Windows 10 & 11If you can still sign in
Do not log out before you have a recovery route, especially if you are using the only device that still has access. Once you are on a known-clean device, work through these steps.
1. Change the password immediately
Choose a long, unique password that has never been used on another account. Do not use your gamer tag, team name, birth date, favorite game, or a variation of the old password. If the attacker changed the email address or recovery details, take screenshots first and then restore them using the provider’s normal security settings.
If you reused the old password anywhere else, change those accounts too. Start with:
- Your primary email account.
- Banking, payment, shopping, and digital-wallet accounts.
- Your mobile-phone carrier account.
- Cloud storage and social-media accounts.
- Password-manager and identity-provider accounts.
- Any service using the same password or the same email address for recovery.
A password manager can generate and store a different password for every service. It does not recover a hacked account by itself, but it makes it practical to replace reused credentials without creating another set of easy-to-guess passwords. Protect the password manager with a strong unique master password and multifactor authentication.
Quick wins for a faster PC:
Repair Windows errors before they cause bigger problemsFix Now →Scan for outdated or missing drivers - takes under a minuteDriver Scan →2. End unfamiliar sessions and remove unknown devices
Open the account’s security area and look for labels such as Devices, Sessions, Where you’re signed in, Recent activity, or Sign out everywhere. Remove devices and sessions you do not recognize. If the provider offers a single “sign out of all devices” option, use it, then sign in again only on devices you trust.
Rank #2
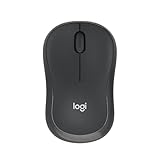
- Pair and Play: With fast, easy Bluetooth wireless technology, you’re connected in seconds to this quiet cordless mouse —no dongle or port required
- Less Noise, More Focus: Silent mouse with 90% reduced click sound and the same click feel, eliminating noise and distractions for you and others around you (1)
- Long-Lasting Battery Life: Up to 18-month battery life with an energy-efficient auto sleep feature, so you can go longer between battery changes (2)
- Comfortable, Travel-Friendly Design: Small enough to toss in a bag; this slim and ambidextrous portable compact mouse guides either your right or left hand into a natural position
- Long-Range: Reliable, long-range Bluetooth wireless mouse works up to 10m/33 feet away from your computer (3)
For a game account, check more than the console or PC currently in front of you. Look for old consoles, gaming PCs, mobile devices, browsers, streaming devices, and third-party launcher sessions. Revoke unfamiliar connections to Discord, Twitch, Google, Microsoft, Apple, Facebook, or other linked identity providers.
3. Restore recovery information
Review the recovery email address, phone number, security questions, trusted devices, and two-step-verification methods. Remove anything added by the attacker and confirm that your own details are correct. Pay particular attention to a new email address: an attacker who controls recovery email may be able to reset the password again after you change it.
Do not assume that changing the main password fixed the problem. An attacker may still have an active session, an app password, an authorized application, or a recovery method that survives the password change.
What’s actually slowing this PC down?
Pick the symptom - the matching free tool is one click away.
4. Inspect connected email settings
Your email account deserves priority because it receives password-reset links for game accounts and other services. In Gmail on the web, review the areas under Settings > See all settings, including:
- Forwarding and POP/IMAP for an address you did not add.
- Filters and Blocked Addresses for rules that hide security emails or mark them as read.
- Accounts and Import, including delegation or “Grant access to your account.”
- Automatic replies, signatures, sent mail, trash, and deleted messages.
Other email services use different labels, but the checks are the same. Search for password-reset emails, security notifications, new-device alerts, deleted messages, forwarding rules, filters, delegates, and automatic replies that you did not create. Remove unauthorized rules and connected apps.
5. Turn on multifactor authentication
Enable multifactor authentication, or MFA, as soon as the account is stable. Any MFA is better than a password alone, but CISA identifies phishing-resistant MFA as the strongest target. Physical security keys are one example; authenticator apps and biometrics are also supported options on many services. Use the strongest method the particular game platform, email provider, or account supports.
After you regain access and confirm that your provider supports it, a FIDO2 hardware security key can be a strong post-recovery option for email, gaming, cloud, and financial accounts. Check whether the account supports the key’s connection type before buying, and consider keeping a second backup key in a safe place. A security key should not be your only recovery method: add another approved recovery option and save backup codes somewhere offline or otherwise separate from the account and device being protected.
Free tools Windows power users keep installed
One-click scans. No signup required.
Never send a one-time code, backup code, or security-key approval to another person. If a login prompt appears that you did not initiate, deny it and change the password again from a clean device.
If you are locked out
Use only the service provider’s official account-recovery flow. Do not pay a stranger who promises instant access, and do not give a third-party recovery service your password or verification codes.
Rank #3

- 【Dual Mode Wireless Bluetooth Mouse】: Switch easily between two devices—connect one via Bluetooth (BT5.2/3.0) and the other using a 2.4G USB receiver. No drivers needed; just plug and play. Enjoy a reliable connection up to 33 feet. Note: You can't use both modes simultaneously; the USB receiver is stored in the mouse.
- 【Rechargeable Wireless Mouse】: Equipped with a 500mAh lithium-ion battery, it charges in 2 hours for over 7 days of use and 30 days on standby. The mouse sleeps after 5 minutes of inactivity to save power and can be woken with any click.
- 【Colorful LED Breathing Light】: Features 7 colorful LED lights that change randomly, adding a fun atmosphere to your workspace.
- 【Portable Mouse】Compact size (4.4 x 2.3 x 1.1 inches) makes it easy to fit in your laptop bag. Lightweight and ergonomic, it's perfect for travel. Contact us anytime for support.
- 【Wide Compatibility】: Works with laptops, PCs, tablets, and smartphones across various operating systems, including Android, Windows, and Mac. Ideal for home, office, and travel.
Recover the email account first when necessary
If the game account uses an email address that you can no longer control, recover that email account first. Otherwise, a criminal may intercept every game-platform reset message. Once the email account is secured, change its password, end unfamiliar sessions, verify recovery details, remove forwarding and filters, and enable MFA before attempting to recover the game account.
If the email account is still secure but the game account is locked, go directly to the game publisher or platform’s hacked account, compromised account, or account recovery page. Provide facts that establish ownership, such as the original email address, previous usernames, approximate account-creation date, transaction IDs, receipts, linked accounts, console IDs, or other information the provider specifically requests. Do not guess at details or submit information through a link sent by a stranger.
Do these 3 things before closing this tab:
1Clear out junk files and repair common Windows errors2Fix the driver behind crashes, sound loss and screen glitches3Repair Windows errors before they cause bigger problemsExamples of official recovery routes
- Google: use Google’s account-recovery flow if the password, recovery phone, or other sign-in details were changed. Google says it does not work with third-party account- or password-recovery services and warns users not to share passwords or verification codes.
- Microsoft: use Microsoft’s official sign-in helper and recent-activity tools. Microsoft states that support agents cannot send password-reset links or access and change account details for you.
- Apple: use a trusted Apple device when possible or Apple’s official web recovery process. Apple notes that some password changes can involve a security delay.
- Social platforms: use the platform’s compromised-account flow rather than a direct message from someone offering recovery. Facebook’s official process includes resetting the password, removing unauthorized devices, reviewing activity and recent emails, deleting unauthorized posts, and enabling two-factor authentication.
- Game platforms: use the publisher or console network’s official support form. Search the provider’s main domain yourself for “hacked account” or “account recovery,” rather than trusting a sponsored result, social-media reply, Discord message, or email link.
Keep the recovery case number and all correspondence. If the provider rejects the first request, use the official appeal or follow-up route and provide consistent ownership information. Recovery times and security holds vary; do not bypass them by handing credentials to an unofficial “helper.”
Inspect what happened to the gaming account
Once you are back in, do not stop at the password screen. Attackers may have used the account to steal money, virtual goods, personal information, or access to other services.
Check these areas
- Purchases and billing: review recent purchases, subscriptions, stored cards, PayPal or other payment methods, wallet balances, gift-card activity, and refunds.
- Inventory and trades: check item transfers, marketplace listings, gifts, trades, rare skins, digital currency, and changes to linked game profiles.
- Messages and social activity: inspect sent messages, deleted messages, friend requests, posts, comments, group memberships, and direct messages for scams sent in your name.
- Linked accounts: review connected console accounts, launchers, social accounts, streaming accounts, developer tools, and third-party applications. Remove anything unfamiliar.
- Profile and privacy: restore the email address, username, display name, profile information, privacy controls, parental controls, and communication settings.
- Cloud data: check cloud saves, screenshots, files, chat history, and other stored data for deletion, downloads, or sharing you did not authorize.
- Subscriptions and devices: look for new subscriptions, family members, household devices, remote-play devices, and registered consoles.
Contact the platform’s official billing or fraud department about unauthorized purchases. Contact the card issuer, bank, payment service, or digital-wallet provider immediately as well. For unauthorized wire transfers or an active theft, speed matters more than completing this checklist.
Check the device that may have enabled the compromise
Account theft can result from a stolen password, phishing, a malicious browser extension, infostealer malware, a reused password, or a stolen login session. Changing the password does not clean an infected computer.
- Use a different known-clean device for recovery if available.
- Update the operating system, browser, and trusted security software.
- Run a complete scan with trusted, up-to-date security software.
- Remove suspicious applications and browser extensions, especially anything installed shortly before the compromise.
- Restart the device and run another check if the security tool recommends it.
- Change important passwords again after the device is clean if you entered them while malware may have been active.
The FTC recommends updating or installing trusted security software, scanning the computer, deleting suspicious software, and restarting before account recovery when malware is suspected. A device-cleanup tool cannot recover a cloud account or remove an attacker from the provider’s servers; the provider’s recovery and session-revocation controls are still required.
Protect other accounts connected to the hacked one
Make a short list of every account connected to the compromised address, password, phone number, device, or sign-in button. Include accounts where you used Sign in with Google, Sign in with Apple, Microsoft, Facebook, or another identity provider. Review saved browser passwords and autofill data, but do not export or share the complete password list.
Rank #4

- Your hand can relax in comfort hour after hour with this ergonomically designed mouse. Its contoured shape with soft rubber grips, gently curved sides and broad palm area give you the support you need for effortless control all day long.
- You’ve got the control to do more, faster. Flipping through photo albums and Web pages is a breeze, especially for right-handers—with three standard buttons plus Back/Forward buttons that you can also program to switch applications, go full screen and more. And side-to-side scrolling plus zoom gives you the power to scroll horizontally and vertically through your music library, maps and Facebook feeds, and zoom in and out of photos and budget spreadsheets with a click.* * Requires Logitech SetPoint software (Windows) or Logitech Control Center software (Mac OS X)
- Two years of battery life practically eliminates the need to replace batteries. ** The On/Off switch helps conserve power, smart sleep mode extends battery life and an indicator light eliminates surprises. ** Battery life may vary based on user and computing conditions.
- The tiny Logitech Unifying receiver stays in your laptop. There’s no need to unplug it when you move around, so there’s less worry of it being lost. And you can easily add compatible wireless mice and keyboards to the same wireless receiver.
Prioritize the accounts in this order:
- Email and identity-provider accounts, because they can reset other services.
- Banking, payment, shopping, payroll, tax, and health-savings accounts.
- Mobile-carrier accounts, especially if text messages are used for recovery. Ask the carrier to review unexpected SIM or number changes and add an account PIN or other protection.
- Cloud storage and password-manager accounts.
- Social, messaging, gaming, creator, and work accounts.
For each account, use a new unique password, end unfamiliar sessions, check recovery information, remove unknown apps, enable MFA, and inspect recent activity. Changing only the game password is not enough if the same password was used on your email or payment account.
If personal or financial information may have been exposed
Escalate the response if the attacker could access your Social Security number, identity document, bank details, tax information, health information, address, or other information that could enable identity theft. Also escalate if the attacker opened accounts, changed payroll details, made purchases, or used your identity.
Recommended Free Tools
For U.S. consumers, IdentityTheft.gov provides an FTC identity-theft report and personalized recovery plan. The FTC recommends checking credit reports, changing passwords, contacting companies where fraud occurred, freezing credit when appropriate, and documenting the recovery process.
A U.S. credit freeze is free, does not affect your credit score, is available to anyone, and remains in place until you lift it. You must place the freeze separately with Equifax, Experian, and TransUnion. A one-year initial fraud alert can be placed with one credit bureau, which must notify the other two. A freeze is generally the stronger choice when you believe someone may try to open new credit in your name.
Paid identity-theft monitoring or recovery service may be useful in a higher-severity case, but it is optional. Start with the free official steps, your bank, the affected companies, the credit bureaus, and IdentityTheft.gov. Do not let a paid service delay a credit freeze, payment cancellation, password change, or fraud report.
Independent reader supportYour contribution helps us test, update, and keep practical guides available for everyone.Preserve evidence and report the incident
Keep a folder containing:
- Original security emails and their full headers when available.
- Screenshots of login alerts, changed settings, recovery attempts, and account activity.
- Transaction records, receipts, unauthorized charges, and payment-provider case numbers.
- Usernames, phone numbers, email addresses, URLs, wallet addresses, and social profiles used by the attacker.
- A timeline showing when you noticed the problem and what actions you took.
- Support tickets, recovery case numbers, bank correspondence, and police-report information.
Do not delete evidence until it is no longer needed by the game provider, bank, insurer, employer, or law enforcement. Do not click a suspicious link merely to capture it; screenshot it or copy its displayed text without opening it.
For U.S. incidents, use the appropriate reporting channel:
- Identity theft: IdentityTheft.gov.
- Fraud or scams: ReportFraud.ftc.gov when applicable.
- Cyber-enabled crime or account-takeover fraud: the FBI’s Internet Crime Complaint Center, commonly called IC3.
- Local crime: local law enforcement when you need a police report for identity-theft recovery, or when the case involves threats, stalking, impersonation, extortion, or another local crime.
IC3 asks for detailed incident and banking information in account-takeover complaints. If fraudulent money transfers are involved, report them to the bank and IC3 immediately.
Best Value

- 【Plug and Play for Home/Office/School】The wireless computer mouse features 2.4GHz connectivity, delivering a stable, interference-free connection up to 32ft. Designed for 𝐦𝐞𝐝𝐢𝐮𝐦 𝐭𝐨 𝐥𝐚𝐫𝐠𝐞 𝐬𝐢𝐳𝐞𝐝 𝐡𝐚𝐧𝐝𝐬, it ensures comfortable use all day. Simply plug in the USB-A receiver for instant pairing—no drivers needed. 📌📌 If the mouse isn’t suitable, place the USB receiver in the battery compartment and return both.
- 【3 Levels Adjustable DPI】This travel USB mouse offers 3 adjustable DPI settings (800, 1200, 1600), allowing you to customize sensitivity for precise design work. Effortlessly switch to match your task and elevate your productivity. 📌 Please remove the film at the bottom of the mouse before use.
- 【Effortless Browsing】Equipped with forward and backward buttons, this computer mice streamlines your workflow, making it easy to navigate through web pages and files with a simple click. 📌Side button does not work on Mac.
- 【Visible Indicator Light】 The pc mouse features a visual indicator for DPI levels and low battery alerts. The red light flashes once for 800 DPI, twice for 1200 DPI, and three times for 1600 DPI. When the battery level is below 10%, the light flashes red until the mouse is completely out of power.
- 【Click to Wake】With smart sleep mode, it saves power by standby after 10 inactive minutes, just 2-3 clicks to wake. This efficient design delivers 3x longer battery life than motion-wake mice. Engineered for durability, its buttons and scroll wheel are tested for 10 million clicks, ensuring long-term reliability and consistent performance.
Warn your friends, teammates, and followers
Tell contacts through a separate channel that the account was compromised. Ask them to ignore recent links, trade requests, money requests, giveaway claims, and urgent messages from the account. Tell them not to share verification codes or approve unexpected login prompts.
If you run a community, stream, clan, guild, or business account, post a short warning through a channel the attacker cannot control. After recovery, review messages, posts, comments, new contacts, cloud files, payment methods, subscriptions, and authorized applications for anything sent or changed during the takeover.
What not to do
- Do not argue with, threaten, or bargain with the attacker.
- Do not pay an unsolicited account-recovery service or “support agent.”
- Do not share passwords, MFA codes, backup codes, recovery keys, screenshots containing secrets, or remote access.
- Do not keep using a computer that may be infected to change every password.
- Do not assume that a password change removed every active session or connected application.
- Do not delete evidence before the provider, bank, insurer, or authorities have what they need.
- Do not close the account before checking billing, purchases, evidence, linked accounts, and recovery options.
Special cases: work, school, business, and creator accounts
If the compromised account belongs to an employer, school, esports organization, business, guild, or creator operation, notify the organization’s IT or security team immediately. An administrator may need to revoke sessions, investigate other affected users, preserve logs, reset application tokens, review forwarding rules, and notify customers or colleagues.
Do not quietly continue using a business or school account after noticing a compromise. The account may have access to shared drives, payment systems, customer information, moderation tools, or other people’s accounts.
After recovery: a practical security check
For the next several days, watch for repeated password-reset emails, new-device alerts, unexpected MFA prompts, recovery-information changes, purchases, messages, and payment activity. Make sure the recovery email itself is protected, MFA is working, backup codes are stored separately, and at least one backup recovery method is available.
Finally, write down which accounts were affected, which passwords were reused, which sessions were revoked, and which reports were filed. That record makes it easier to spot a second compromise and to prove the timeline if a provider, bank, insurer, or law-enforcement agency asks for details.
The Tool Desk
Outbyte PC Repair FREEClear out junk files and repair common Windows errorsFree Scan →Outbyte Driver Updater FREEScan for outdated or missing drivers - takes under a minuteDriver Scan →Frequently Asked Questions
Should I message the person who hacked my account?
No. Do not reply, threaten, bargain, send money, or provide information. Save evidence and use the provider’s official recovery and reporting channels instead.
What should I do if both my game account and email account were hacked?
Use a known-clean device and recover the email account first, because it receives password-reset messages for the game account. Then secure the email account, recover the game account through its official compromised-account process, revoke sessions, and enable MFA.
Can antivirus software recover my hacked gaming account?
No. A trusted, up-to-date security tool can help find malware on the device, but it cannot restore a cloud account or remove an attacker from the provider’s systems. You still need the official account-recovery process, password changes, session revocation, and MFA.
Should I pay someone who says they can recover my account?
Usually not, especially if they contacted you first. Treat unsolicited recovery offers as scams. Legitimate recovery should begin through the game platform, email provider, console network, or other service’s official website or app.
Windows Errors? Fix Them Before They Spread
Repair common Windows errors and clear accumulated junk for a smoother, more stable PC - no reinstall needed.Free scan · no reinstallOutdated Drivers Are Slowing You Down
One free scan finds every outdated or missing driver and matches the right update for your exact hardware.Free scan · exact hardware matchThe Bottom Line
Contain the damage first: stop clicking suspicious messages, use a clean device, contact your bank about financial activity, and use only official recovery channels. Then change the password, revoke sessions, restore recovery settings, inspect the account and linked services, enable MFA with backup recovery options, report the incident, and warn your contacts.
Quick Recap
Product prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on Amazon at the time of purchase will apply.




